An engineering breakdown of our autonomous exposure validation engine, tri-layer scheduling, and production-safe guardrail sanitizer. Verified reports delivered in 4–8 hours.
Every automated run follows a strict, deterministic sequence designed for precision and safety.
Enter your target domains and IP ranges. NeuraPent locks strict CIDR boundaries, verifies ownership authorizations, and initializes policy constraints before sending a single probe.
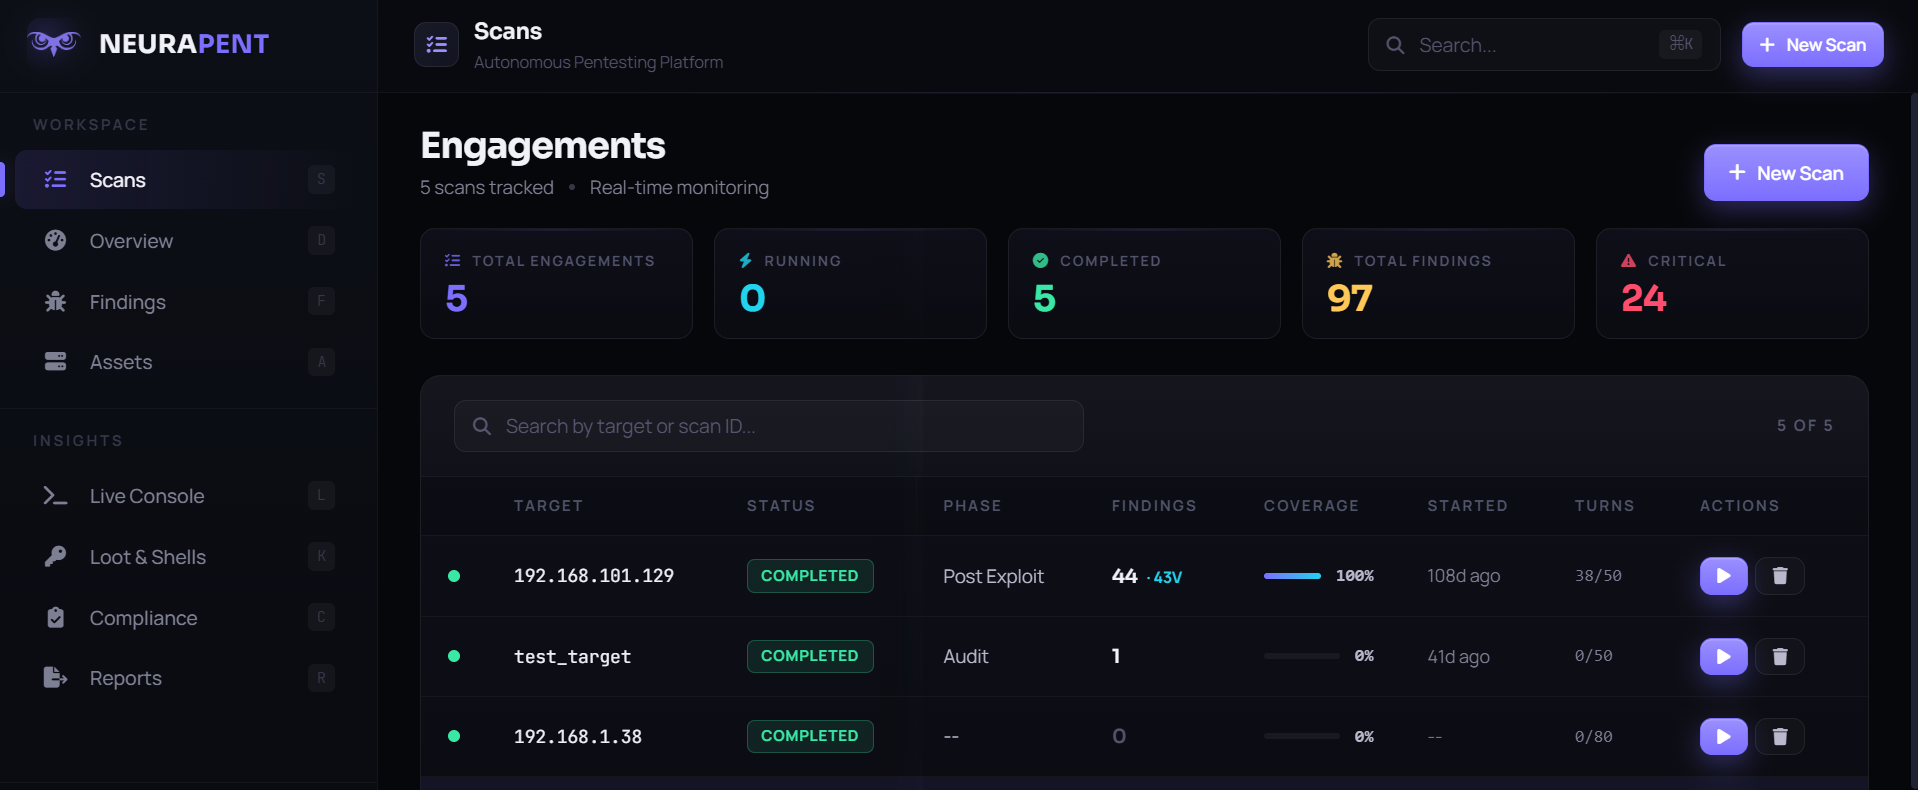
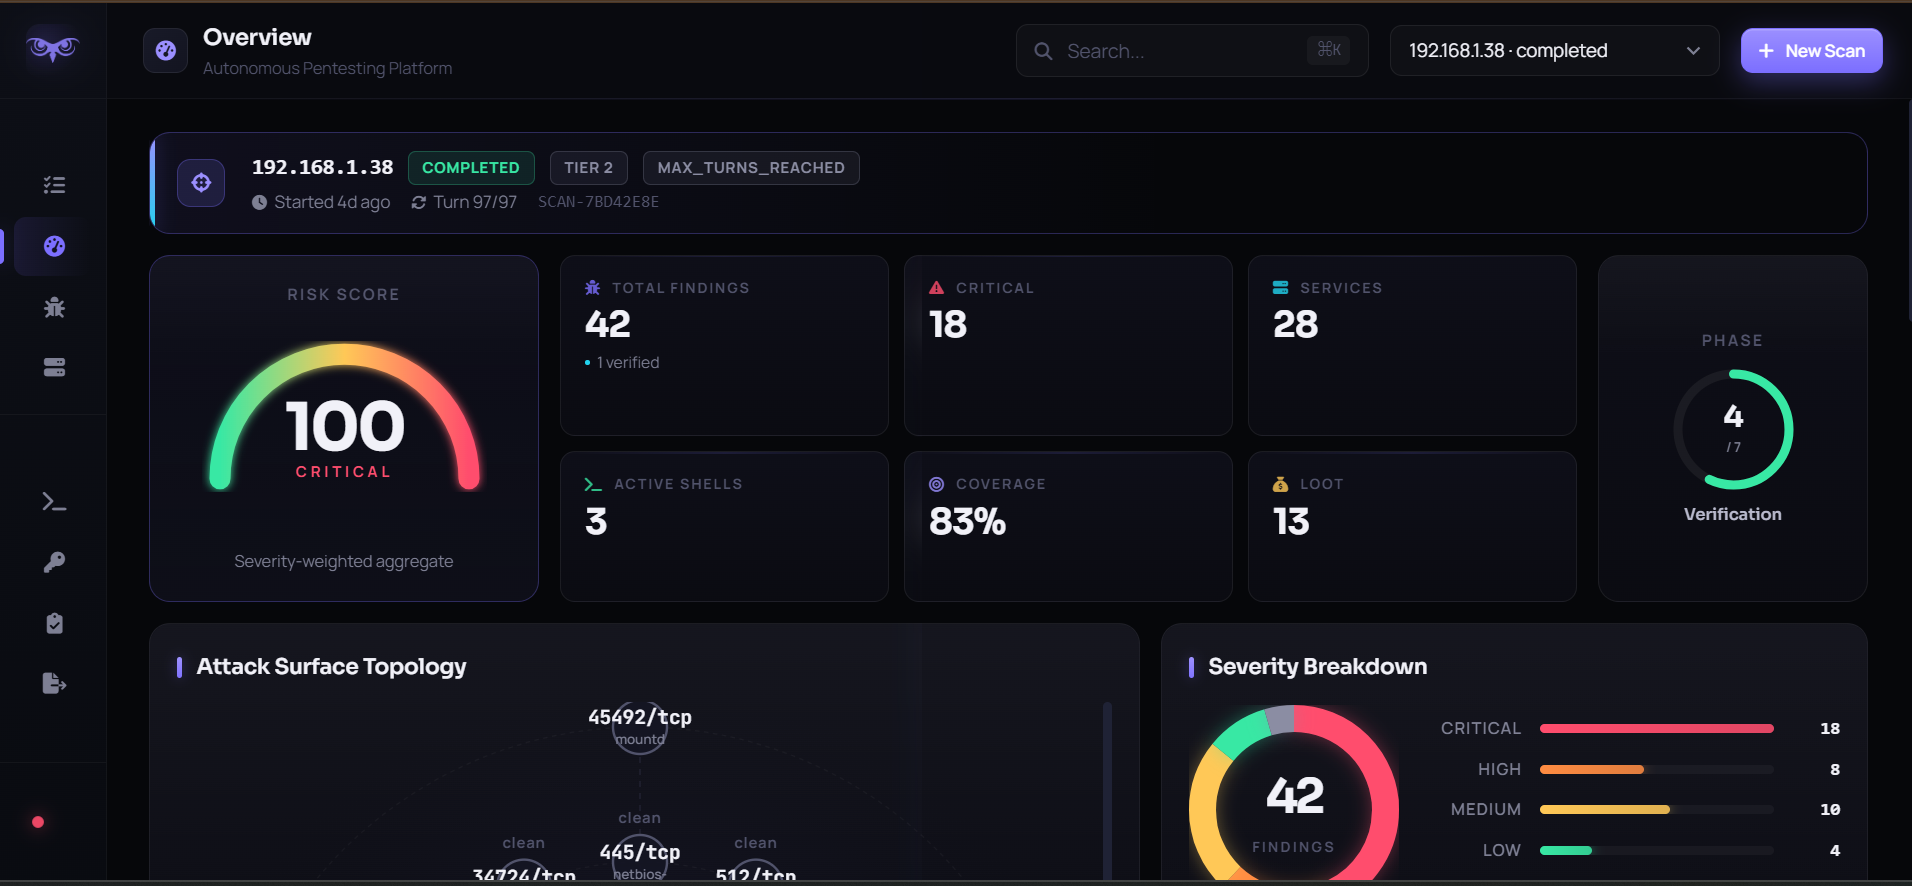
Autonomous discovery workers scan all 65,535 TCP ports to catalog public assets. Discovered services are fingerprinted for protocol versions, headers, cloud configurations, and API schemas.
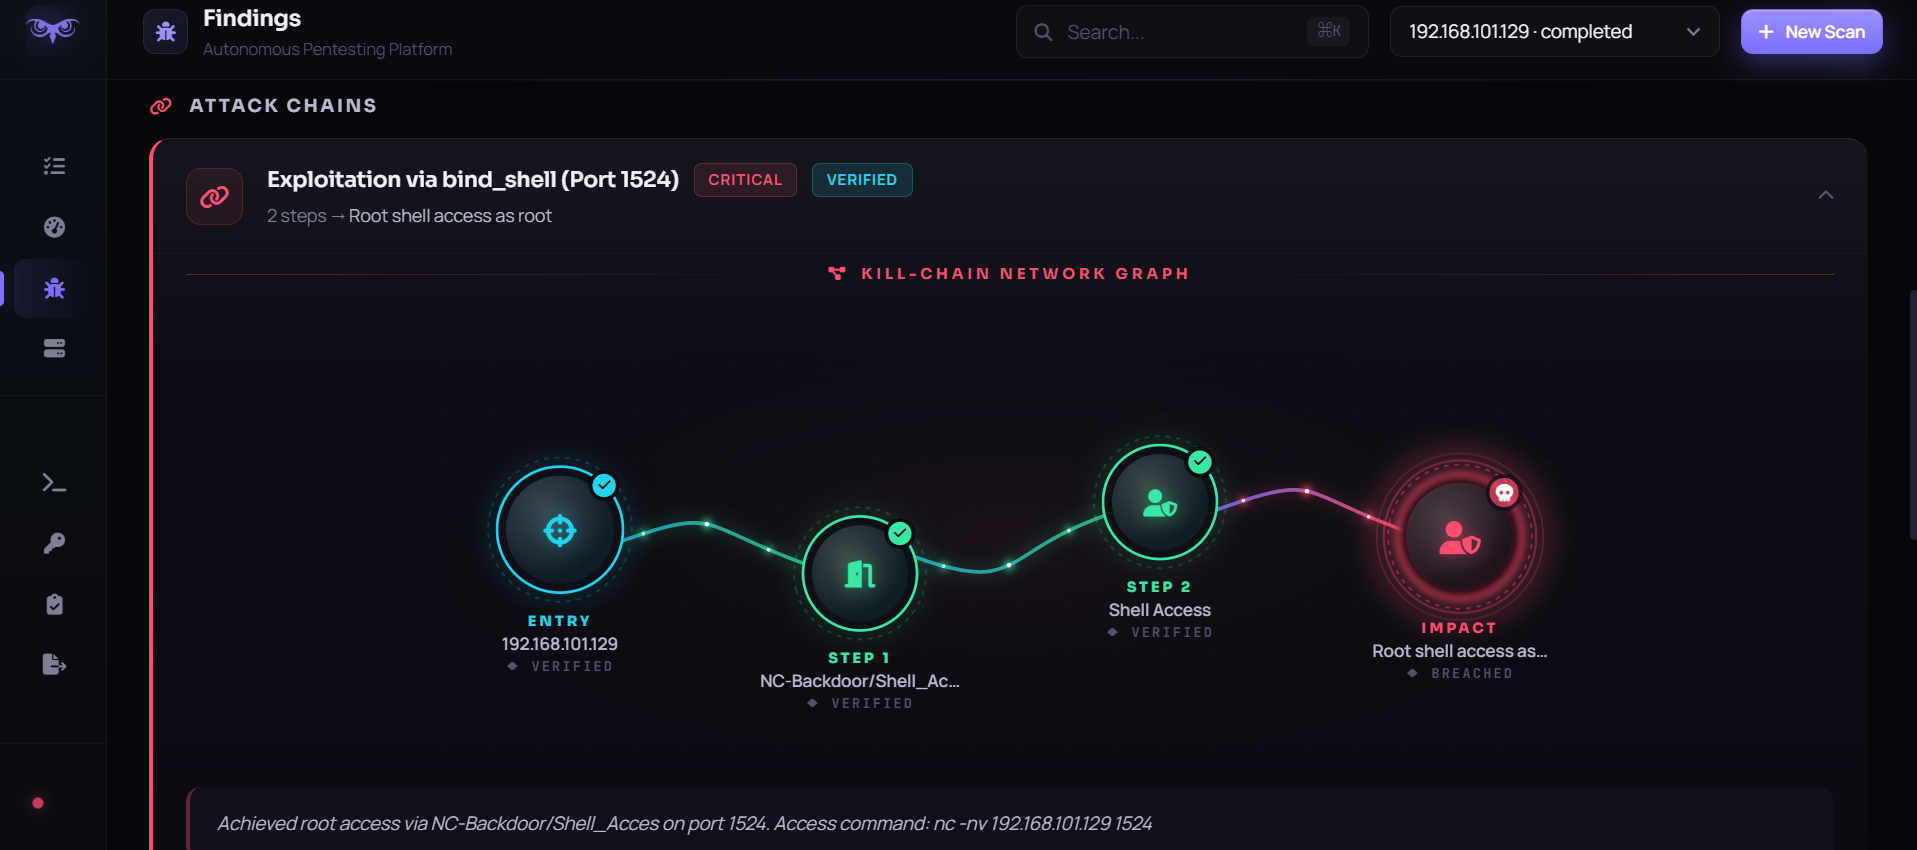
Rather than reviewing vulnerabilities in isolation, NeuraPent models lateral attacker movement. Discovered tokens, configuration leaks, and API flaws are chained together into multi-step exploit sequences.
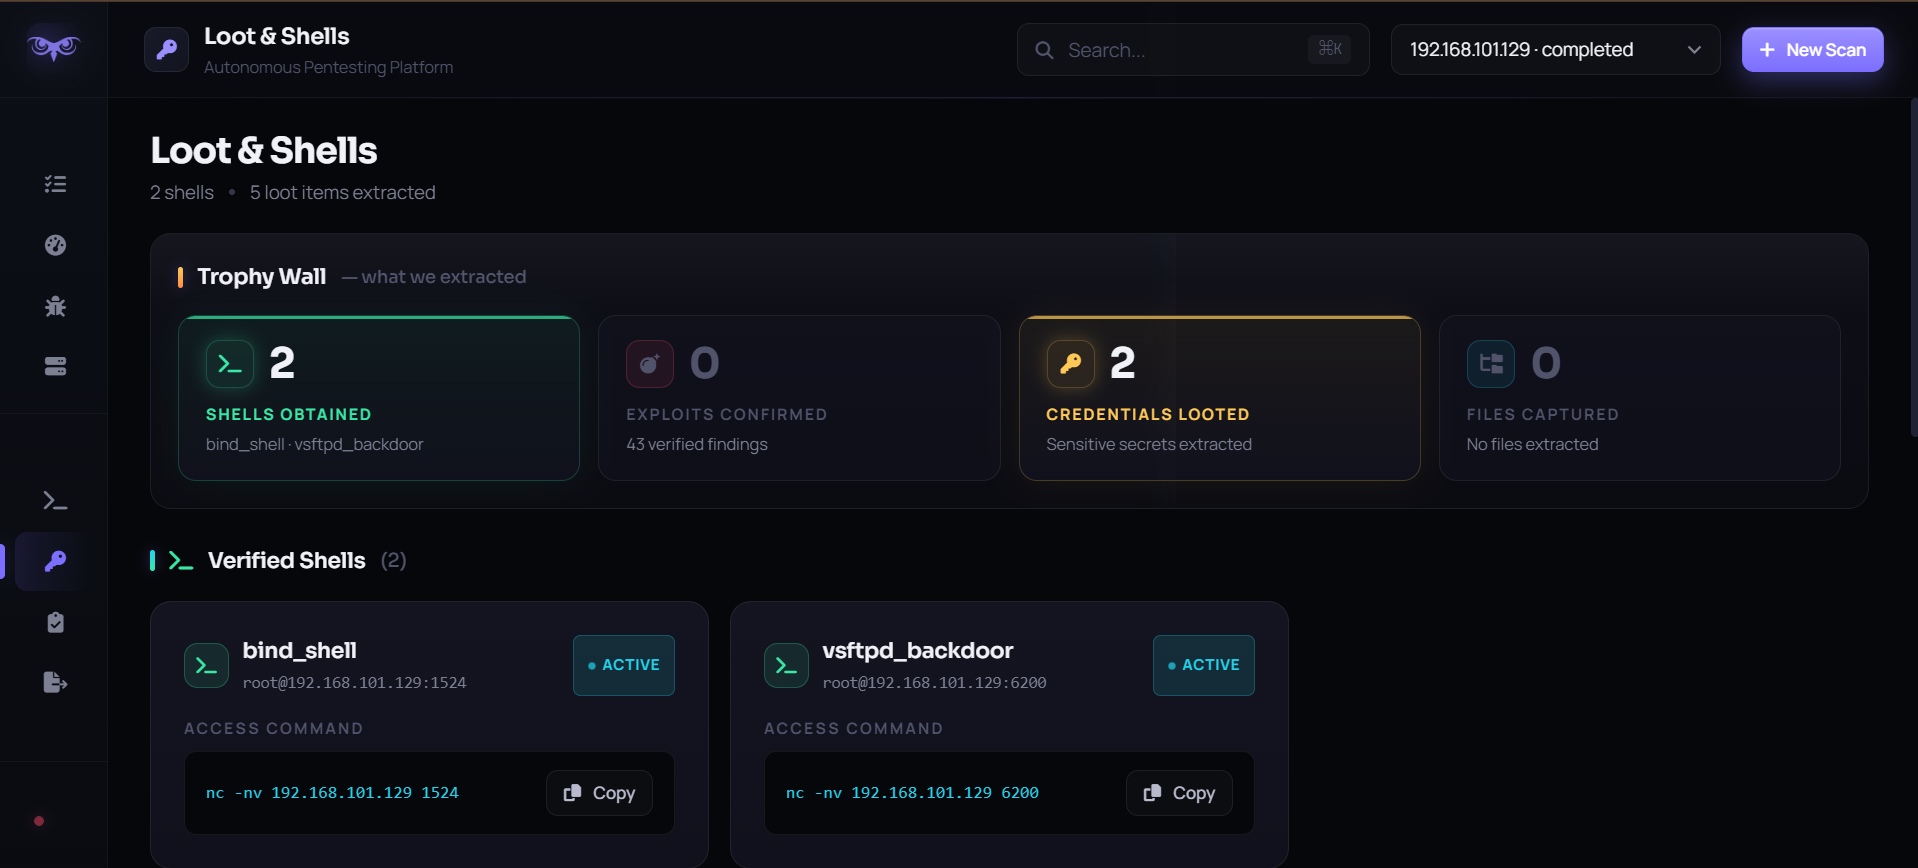
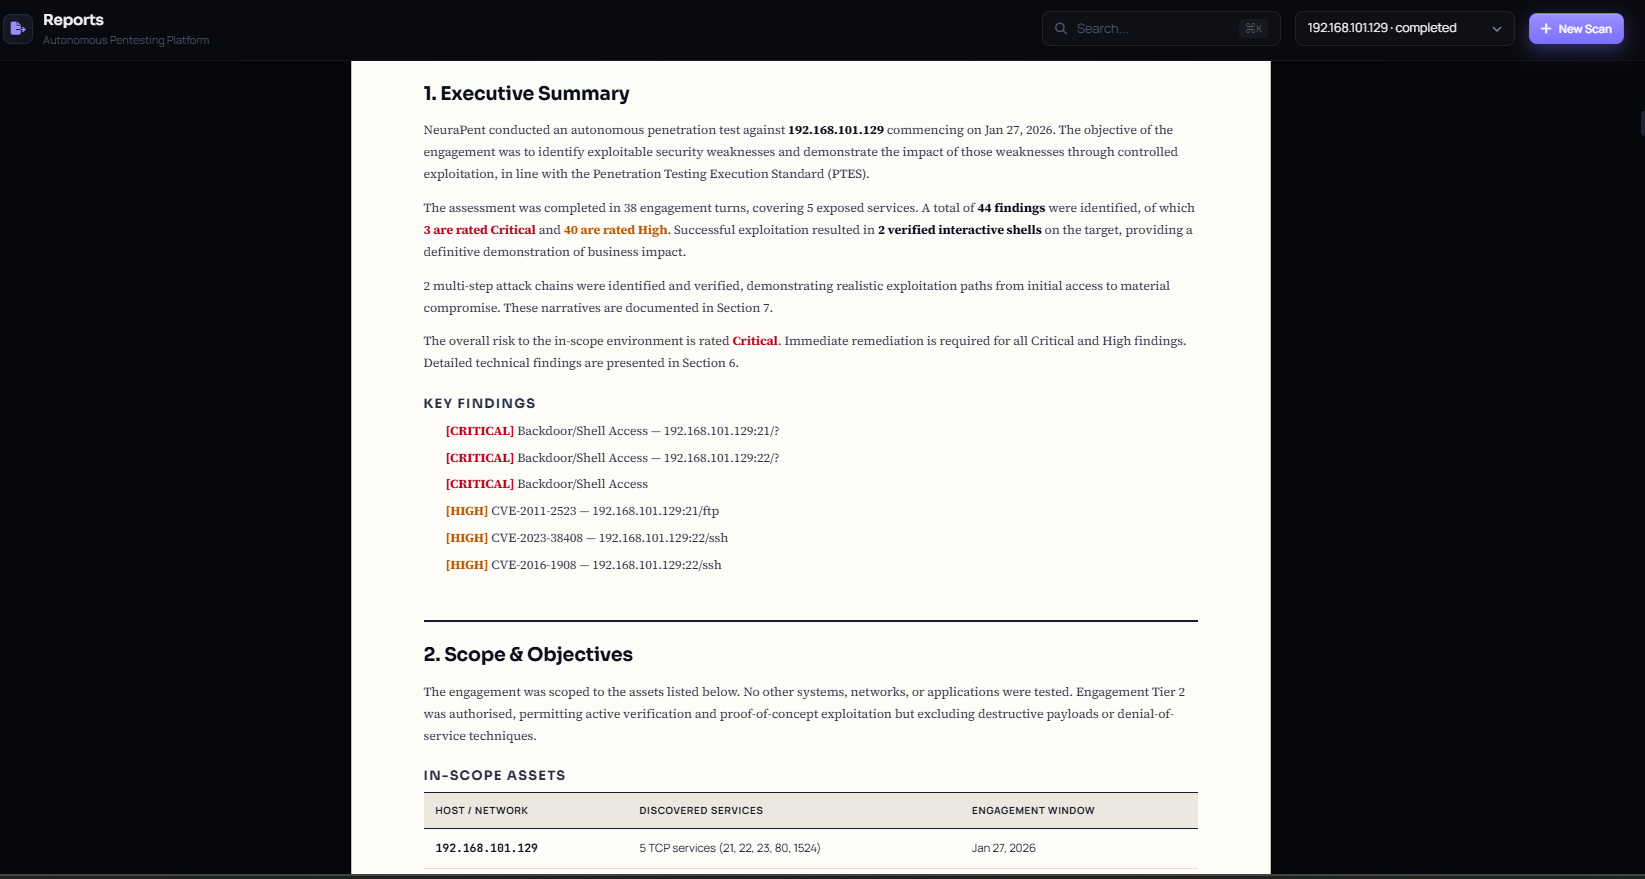
Specialized verification agents dispatch localized, safe proof-of-concept scripts. We capture full HTTP request and response evidence to verify exploitability with zero false positives and zero downtime.
Generate compliance-mapped executive reports and developer-ready code fix diffs delivered in 4–8 hours. Run 1-click automated re-verification scans to confirm that vulnerabilities are definitively resolved.
How our backend isolates state, coordinates agents, and executes verification.
The single source of truth tracking target boundaries, discovered ports, credentials, and the graph of validated exploit paths. Ensures deterministic state across runs and prevents testing loops.
A reactive task queue evaluating emerging findings in real time. Dispatches specialized subagents to explore attack paths dynamically based on priority, confidence, and target safety criteria.
Modular specialist agents (Recon, Auth Fuzzer, CVE Verifier, Attack Chainer, and Report Compiler) optimized via DSPy to synthesize safe, non-destructive proofs of concept.
To ensure total safety and compatibility with enterprise firewall filters and LLM policies, NeuraPent translates aggressive exploit patterns into verified, safe proof equivalents before execution.
| Adversarial Security Term | Safe Translation | Sanitized Operational Definition |
|---|---|---|
| Exploit | Demonstrate impact of exposure | |
| Shell / RCE | Callback command channel validation | |
| Payload | Safe proof-of-concept input | |
| Privilege Escalation | Privilege boundary audit | |
| Lateral Movement | Cross-host capability verification |
Deploy autonomous penetration testing across your cloud servers and APIs in minutes.